THE IDENTITY AND CONTINUITY LAYER
FOR AUTONOMOUS SYSTEMS

It provides deterministic identity, lifecycle continuity, and governance enforcement for agents operating across distributed environments.
It provides deterministic identity, lifecycle continuity, and governance enforcement for agents operating across distributed environments.

What ACELOGIC Does
ACELOGIC™ establishes canonical identity for every autonomous agent.
Agents within ACELOGIC™ are born and governed through:
⊘
ACEAGENT™
Persistent Canonical Identity
A unique, persistent identity that remains bound to the agent across authorized runtime changes, recovery, and deployment environments.
↻
CANONICAL AGENT ENFORCEMENT
One Identity. No Conflicting Claimants.
Bring persistent agent identity and governance to authorized external execution environments.
⇄
DIMENSIONAL AGENT SYSTEMS (DAS)
Mission-Critical Assurance
Higher-assurance identity, governance, continuity, and validation architecture for mission-critical and high-consequence autonomous systems.
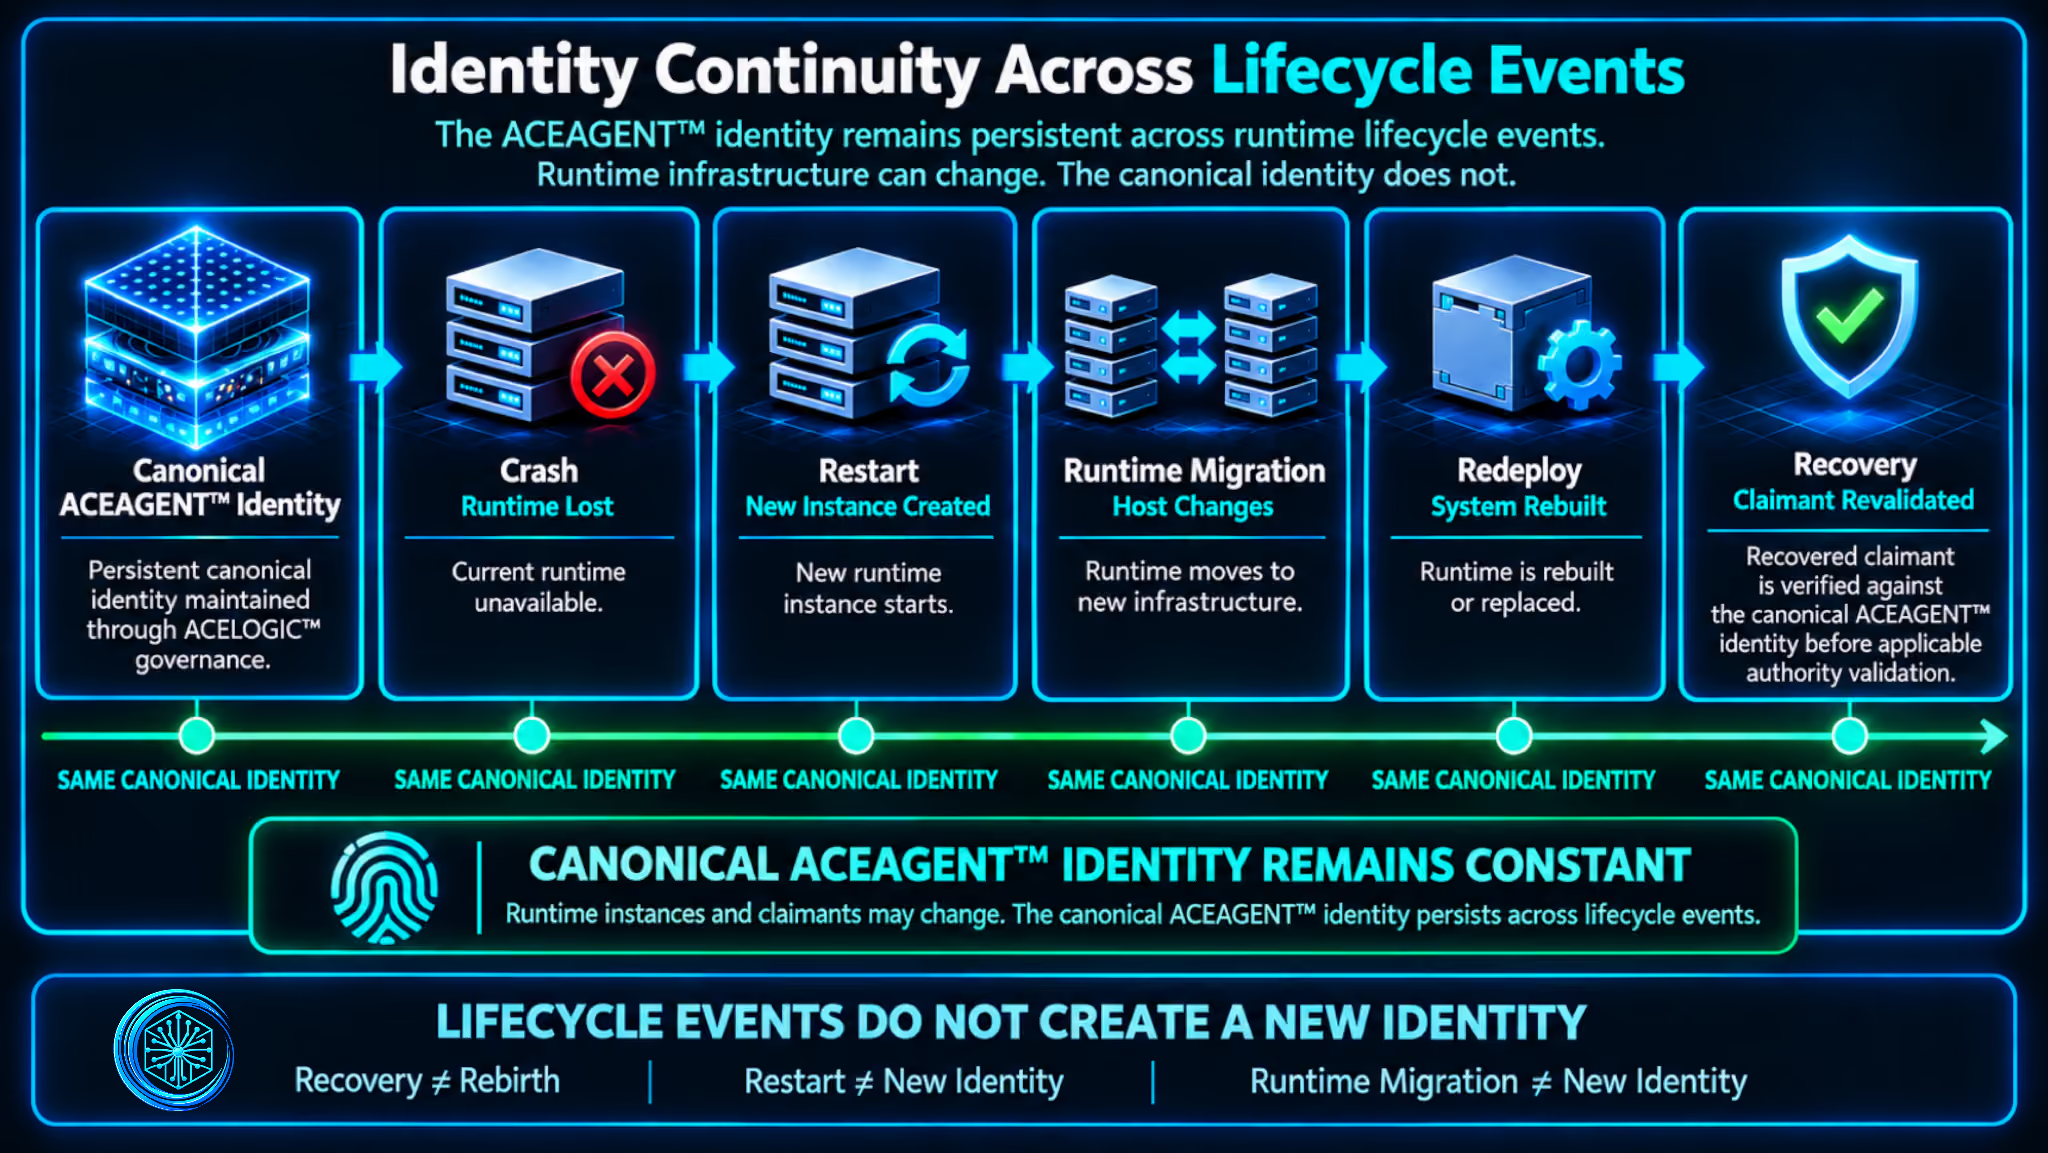
LIFECYCLE EVENTS DO NOT CREATE A NEW IDENTITY

Has a one-of-one canonical deterministic identity. Persists across restarts, migrations, and environments.
Cannot be duplicated, forked, or impersonated. Maintains verifiable canonical lineage over time
WHY IDENTITY MATTERS
Identity is assumed, not enforced.
Modern systems track:

Process

Data

Infrastructure
But they do not enforce identity continuity.
When autonomous systems restart or scale:
⚠
Multiple instances can claim the same authority
⚠
Execution becomes ambiguous
⚠
Accountability is lost
IDENTITY AS INFRASTRUCTURE
ACELOGIC™ operates as a control-plane layer beneath applications and runtimes.
It is not:
✕
A model
✕
A workflow tool
✕
A data platform
IT IS THE IDENTITY, GOVERNANCE AND CONTINUITY INFRASTRUCTURE FOR AUTONOMOUS SYSTEMS.
ACELOGIC SOLVES THIS
ACELOGIC™ enforces deterministic identity and continuity at the infrastructure level.
THIS RESULTS IN
Duplicate execution
Conflicting authority
State inconsistency
System instability
Regulatory exposure
CONTINUITY NOTARY™ IN PRACTICE
While CONTINUITY NOTARY™ is independently licensable, it is actively implemented within NXQ's broader architecture.

AGENT ASSURANCE MODEL
ACELOGIC™ DEFINES A NEW CLASS OF AUTONOMOUS SYSTEMS:
ACELOGIC™ separates canonical agent identity from the level of assurance applied to that identity.
ACEAGENT™

Every governed agent begins with a persistent canonical identity established through Genesis.
DIMENSIONAL AGENT SYSTEMS (DAS)

For mission-critical and high-consequence environments, ACEAGENT™ identities can operate under a higher-assurance architecture spanning identity, governance, continuity, validation, and execution controls.
CANONICAL ENFORCEMENT

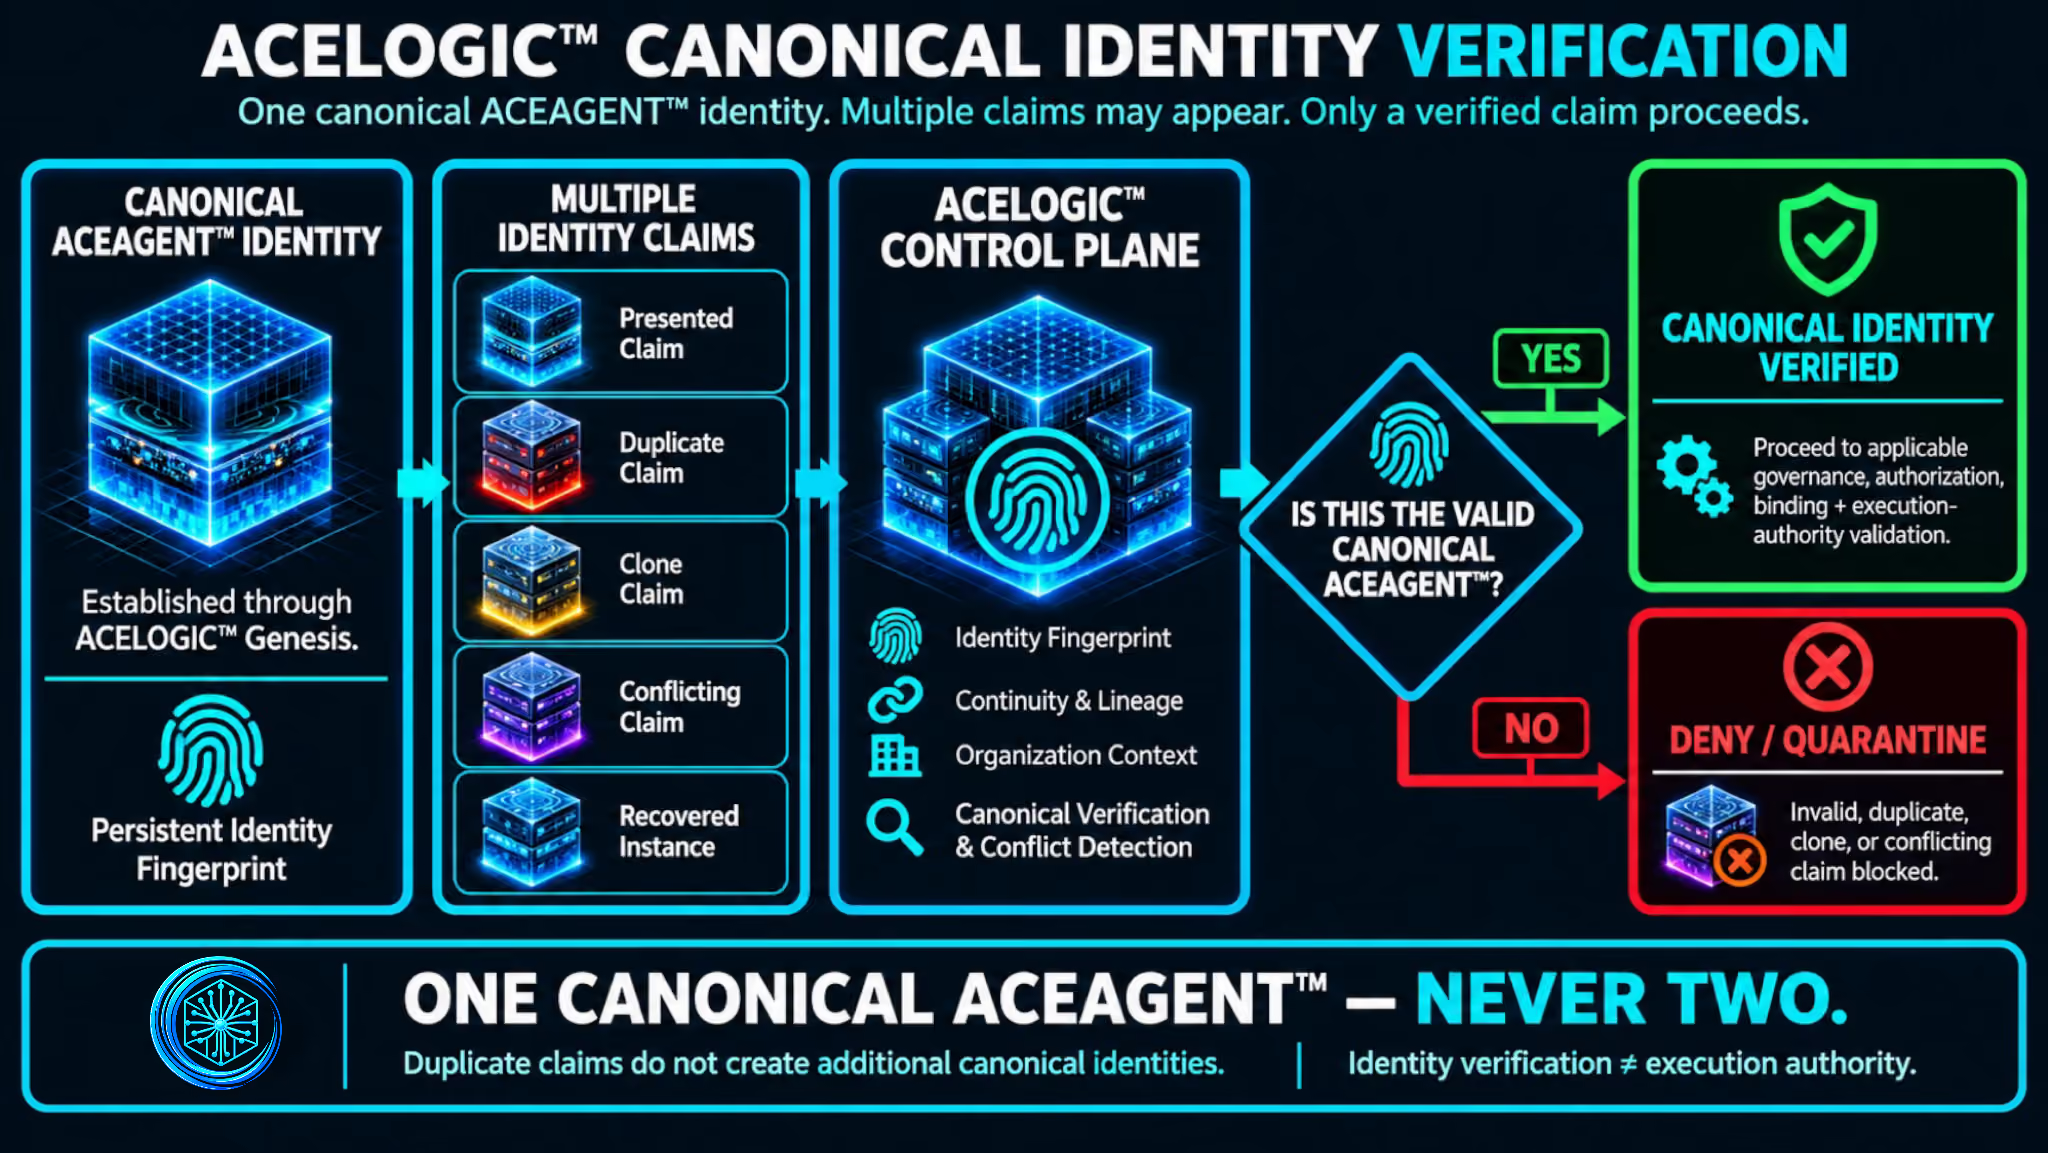
The ACELOGIC™ Control Plane validates which runtime is authorized to represent the canonical agent and rejects or quarantines conflicting claimants.

HOW ACELOGIC WORKS
CONTINOUS, AUDITABLE IDENTITY RECORD
AGENT GENESIS
Agents are born as canonical ACEAGENT™ identities through the ACELOGIC™ Genesis process Gates 1-6.
Each ACEAGENT™ receives:

A deterministic, one-of-one Identity Fingerprint
A unique Agent ID
A bound mission and purpose
An initial continuity state
Canonical ownership and organizational binding
Governed identity metadata
DIMENSIONAL AGENT SYSTEMS (DAS) — HIGHER ASSURANCE
For mission-critical and high-assurance environments, Dimensional Agent Systems extend the standard Genesis architecture through Gates 1–9.
The higher-assurance DAS path adds:
AnchorChain™
External anchoring of continuity-critical cryptographic evidence
CVR™
Structured continuity-verification evidence
Continuity Authority Gate™
Highest-assurance continuity control point
SHA3-512 Covenant Hash
Cryptographic artifact for the applicable Gates 1-9 path
CONTINUITY ENFORCEMENT
ACELOGIC™ ensures identity continuity across Restarts, Failovers, Migrations, and Redeployments.

Only the canonical identity is permitted to continue execution.
Execution authority is granted only to the canonical identity.
IDENTITY BINDING
IDENTITY IS BOUND TO THE AGENT, NOT THE RUNTIME.
→ Identity is not session-based
→ Identity is not environment-dependent
→ Identity persists across all deployments
Identity is canonical and singular across all environments.
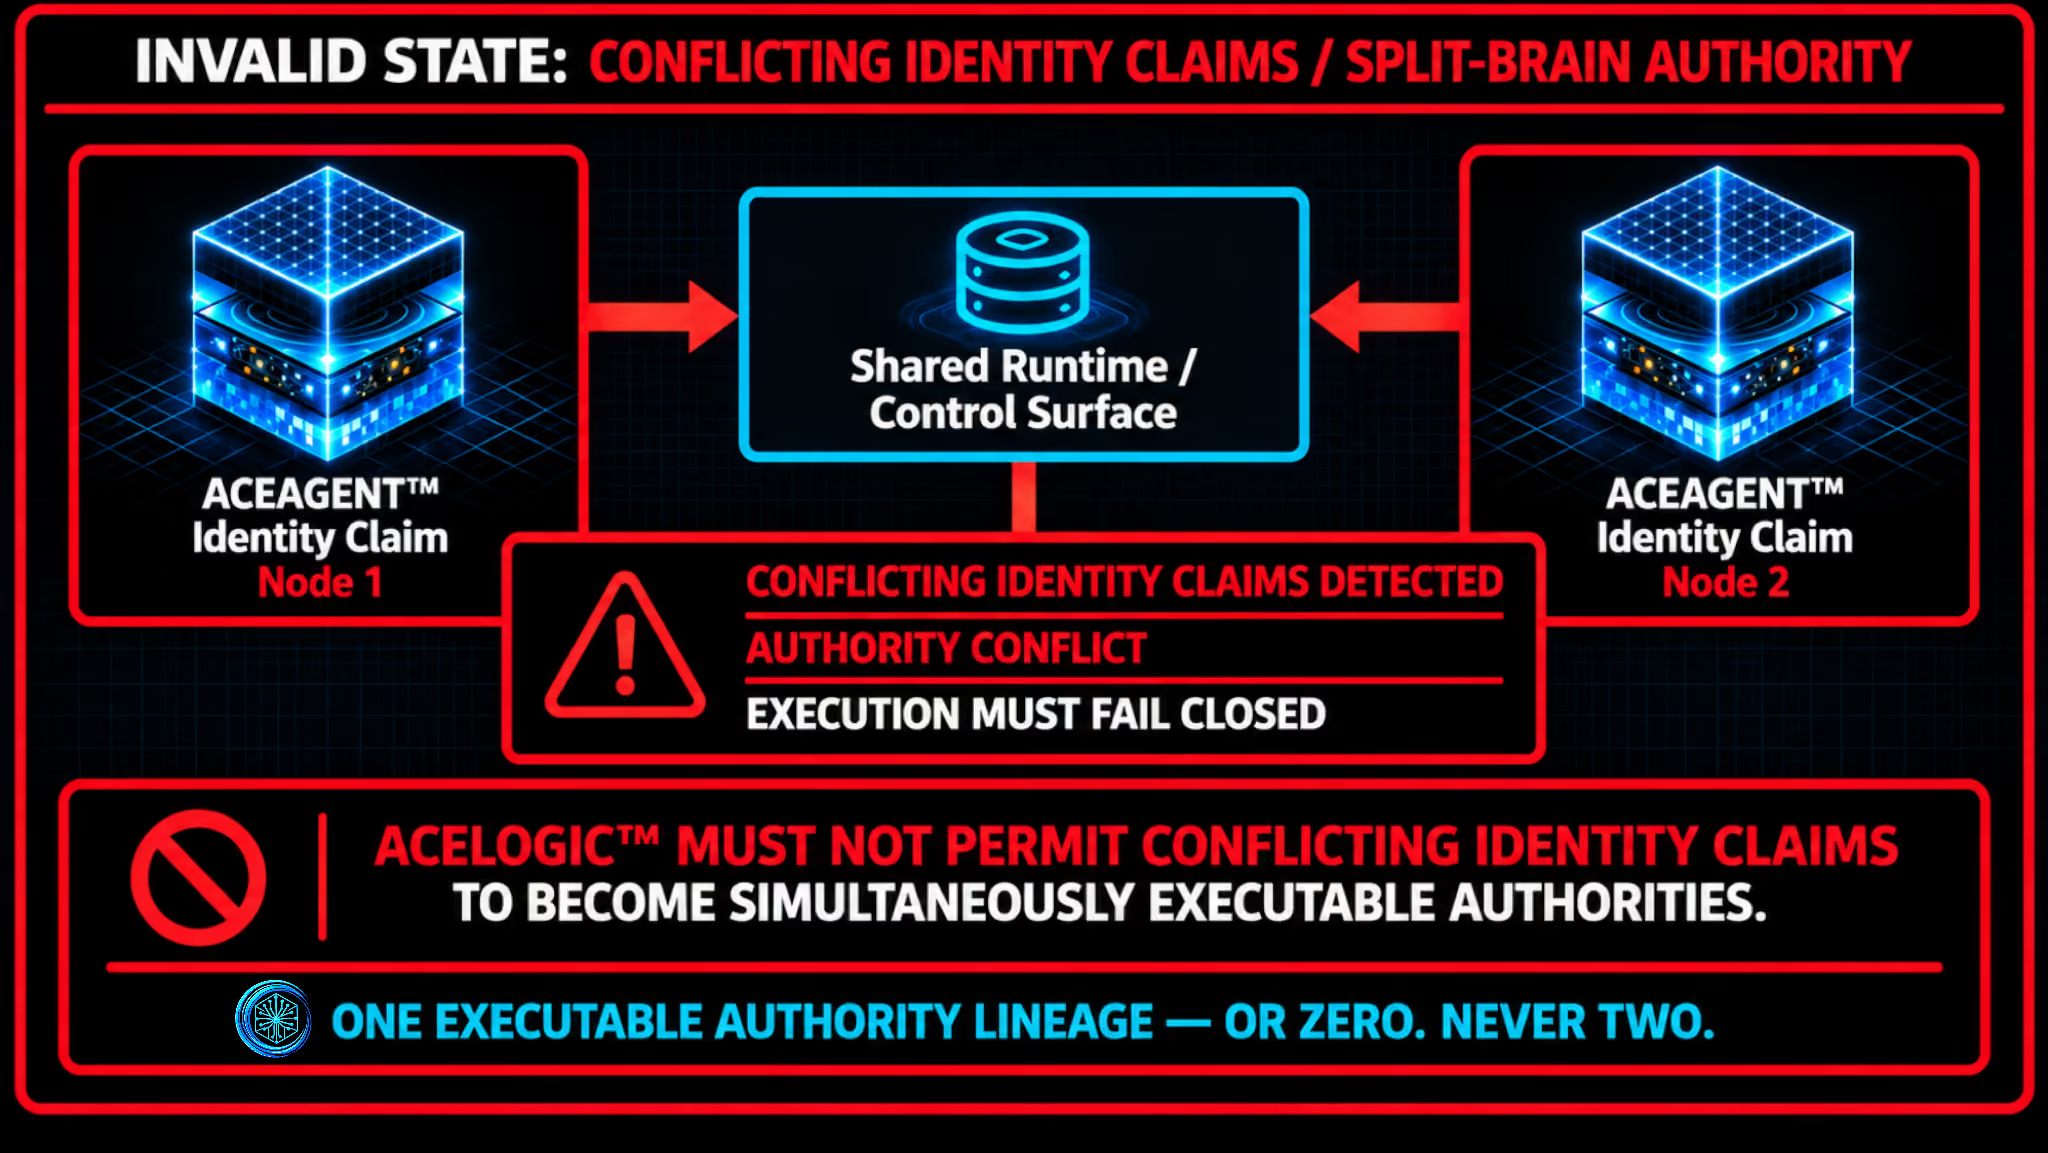
FORK & CLONE PREVENTION
Duplicate agents are detected
Unauthorized forks are rejected
Cloned identities are quarantined
Split-brain execution is prevented
LINEAGE VERIFICATION
Every agent maintains a verifiable canonical history tracking all transformations.
Genesis (creation)
State transitions
Execution events
Governance updates
This produces a continuous, auditable identity record.


IDENTITY ESTABLISHED AT GENESIS
REMAINS CANONICAL
THROUGH EXECUTION, CONTINUITY, AND SETTLEMENT.

WHAT THIS ENABLES
A RESOLVED IDENTITY FOUNDATION
By establishing a static authority loop at the infrastructure level, ACELOGIC™ enables durable capabilities for agents that traditionally execute ephemerally.
Agents become persistent, canonical identity-bound entities
Mission-critical agents can operate under higher-assurance Dimensional Agent Systems (DAS)
Execution becomes identity-bound and attributable
Agent lineage and governance become verifiable and auditable
Autonomous systems become governable across distributed environments

INTEGRATION WITH EXECUTION
ACEPLACE
ACELOGIC™ establishes canonical identity and governance across authorized execution environments. Use ACEPLACE™ as the native deterministic runtime, or integrate ACELOGIC™ with your existing execution infrastructure.
01
ACELOGIC™
Establishes who the agent is
02
CONTROL PLANE
Validates whether the required identity, governance, and authority context is valid
03
ACEPLACE™
Native environment for governed execution
04
EXTERNAL RUNTIMES
Integrate through validation, authorization, and binding
TWO INTEGRATION
PATHS
PATH 01
ACELOGIC™ + ACEPLACE™
Native identity, governance, and deterministic execution.
PATH 02
ACELOGIC™ + YOUR INFRASTRUCTURE
Bring persistent agent identity and governance to authorized external execution environments.

KEEP YOUR INFRASTRUCTURE. ADD IDENTITY + GOVERNANCE FOR AUTONOMOUS SYSTEMS.

COMPLIANCE BY DESIGN
Each agent is established with:
→ Defined authority boundaries
→ Jurisdiction constraints
→ Mission and purpose scope
→ Organizational and ownership context
Execution is governed by:
→ Identity verification
→ Policy and entitlement checks
→ Runtime authorization & binding
→ Bounded execution authority
This supports:
→ Policy-aligned execution
→ Verifiable accountability
→ Auditable decision and execution evidence
→ Controlled execution environments

DATA INDEPENDENCE
ACELOGIC™ operates strictly on identity and continuity, not content or computation.
ACELOGIC™ does not access:
Prompts
Model outputs
Internal data

M2M COORDINATION
Machine-to-Machine Coordination
Integrated natively with MACHINE GRAMMAR™ primitives, ACELOGIC™ enables structured, policy-controlled interaction loops:
Deterministic authority routing
Identity-aware coordination loops
Verifiable execution paths and handoffs

Operation
Cross-Environment Operation
ACELOGIC™ maintains identity continuity across:
Public cloud (AWS, Azure, GCP)
Private and sovereign infrastructure
Edge environments
Physical autonomous systems
IDENTITY REMAINS CONSISTENT REGARDLESS OF EXECUTION ENVIRONMENT.
LICENSING & DEPLOYMENT
ACELOGIC™ supports deployment models ranging from research and development through enterprise and sovereign infrastructure.
01
evaluation
RESEARCH — Evaluation & Validation
Research and evaluation access. Architecture testing and validation. Non-production environments
02
developer
BUILDER — Commercial Runtime License
Build and integrate governed agent systems. ACELOGIC™ identity and Control Plane services. Development and commercial deployment pathways
03
business
GROWTH — Production Operations
Production autonomous-system deployments. Expanded organizational governance. Managed identity and enforcement infrastructure
04
dedicated
ENTERPRISE — Private Runtime Infrastructure
Enterprise-controlled deployment environments. Private infrastructure integration. Advanced governance and deployment controls
05
restricted
SOVEREIGN — Sovereign Runtime Infrastructure
Customer-controlled infrastructure. Regulated and jurisdiction-sensitive environments. Private and sovereign deployment architectures
Core Principle
Identity must be deterministic.
Continuity must be provable.

OUTCOMES
ACELOGIC™ transforms autonomous agents into:

Canonical identities
Verifiable entities
Governed actors
Infrastructure components
Public Reference Architecture